
Devcon 8, It's a Wrap!
by Péter Szilágyi
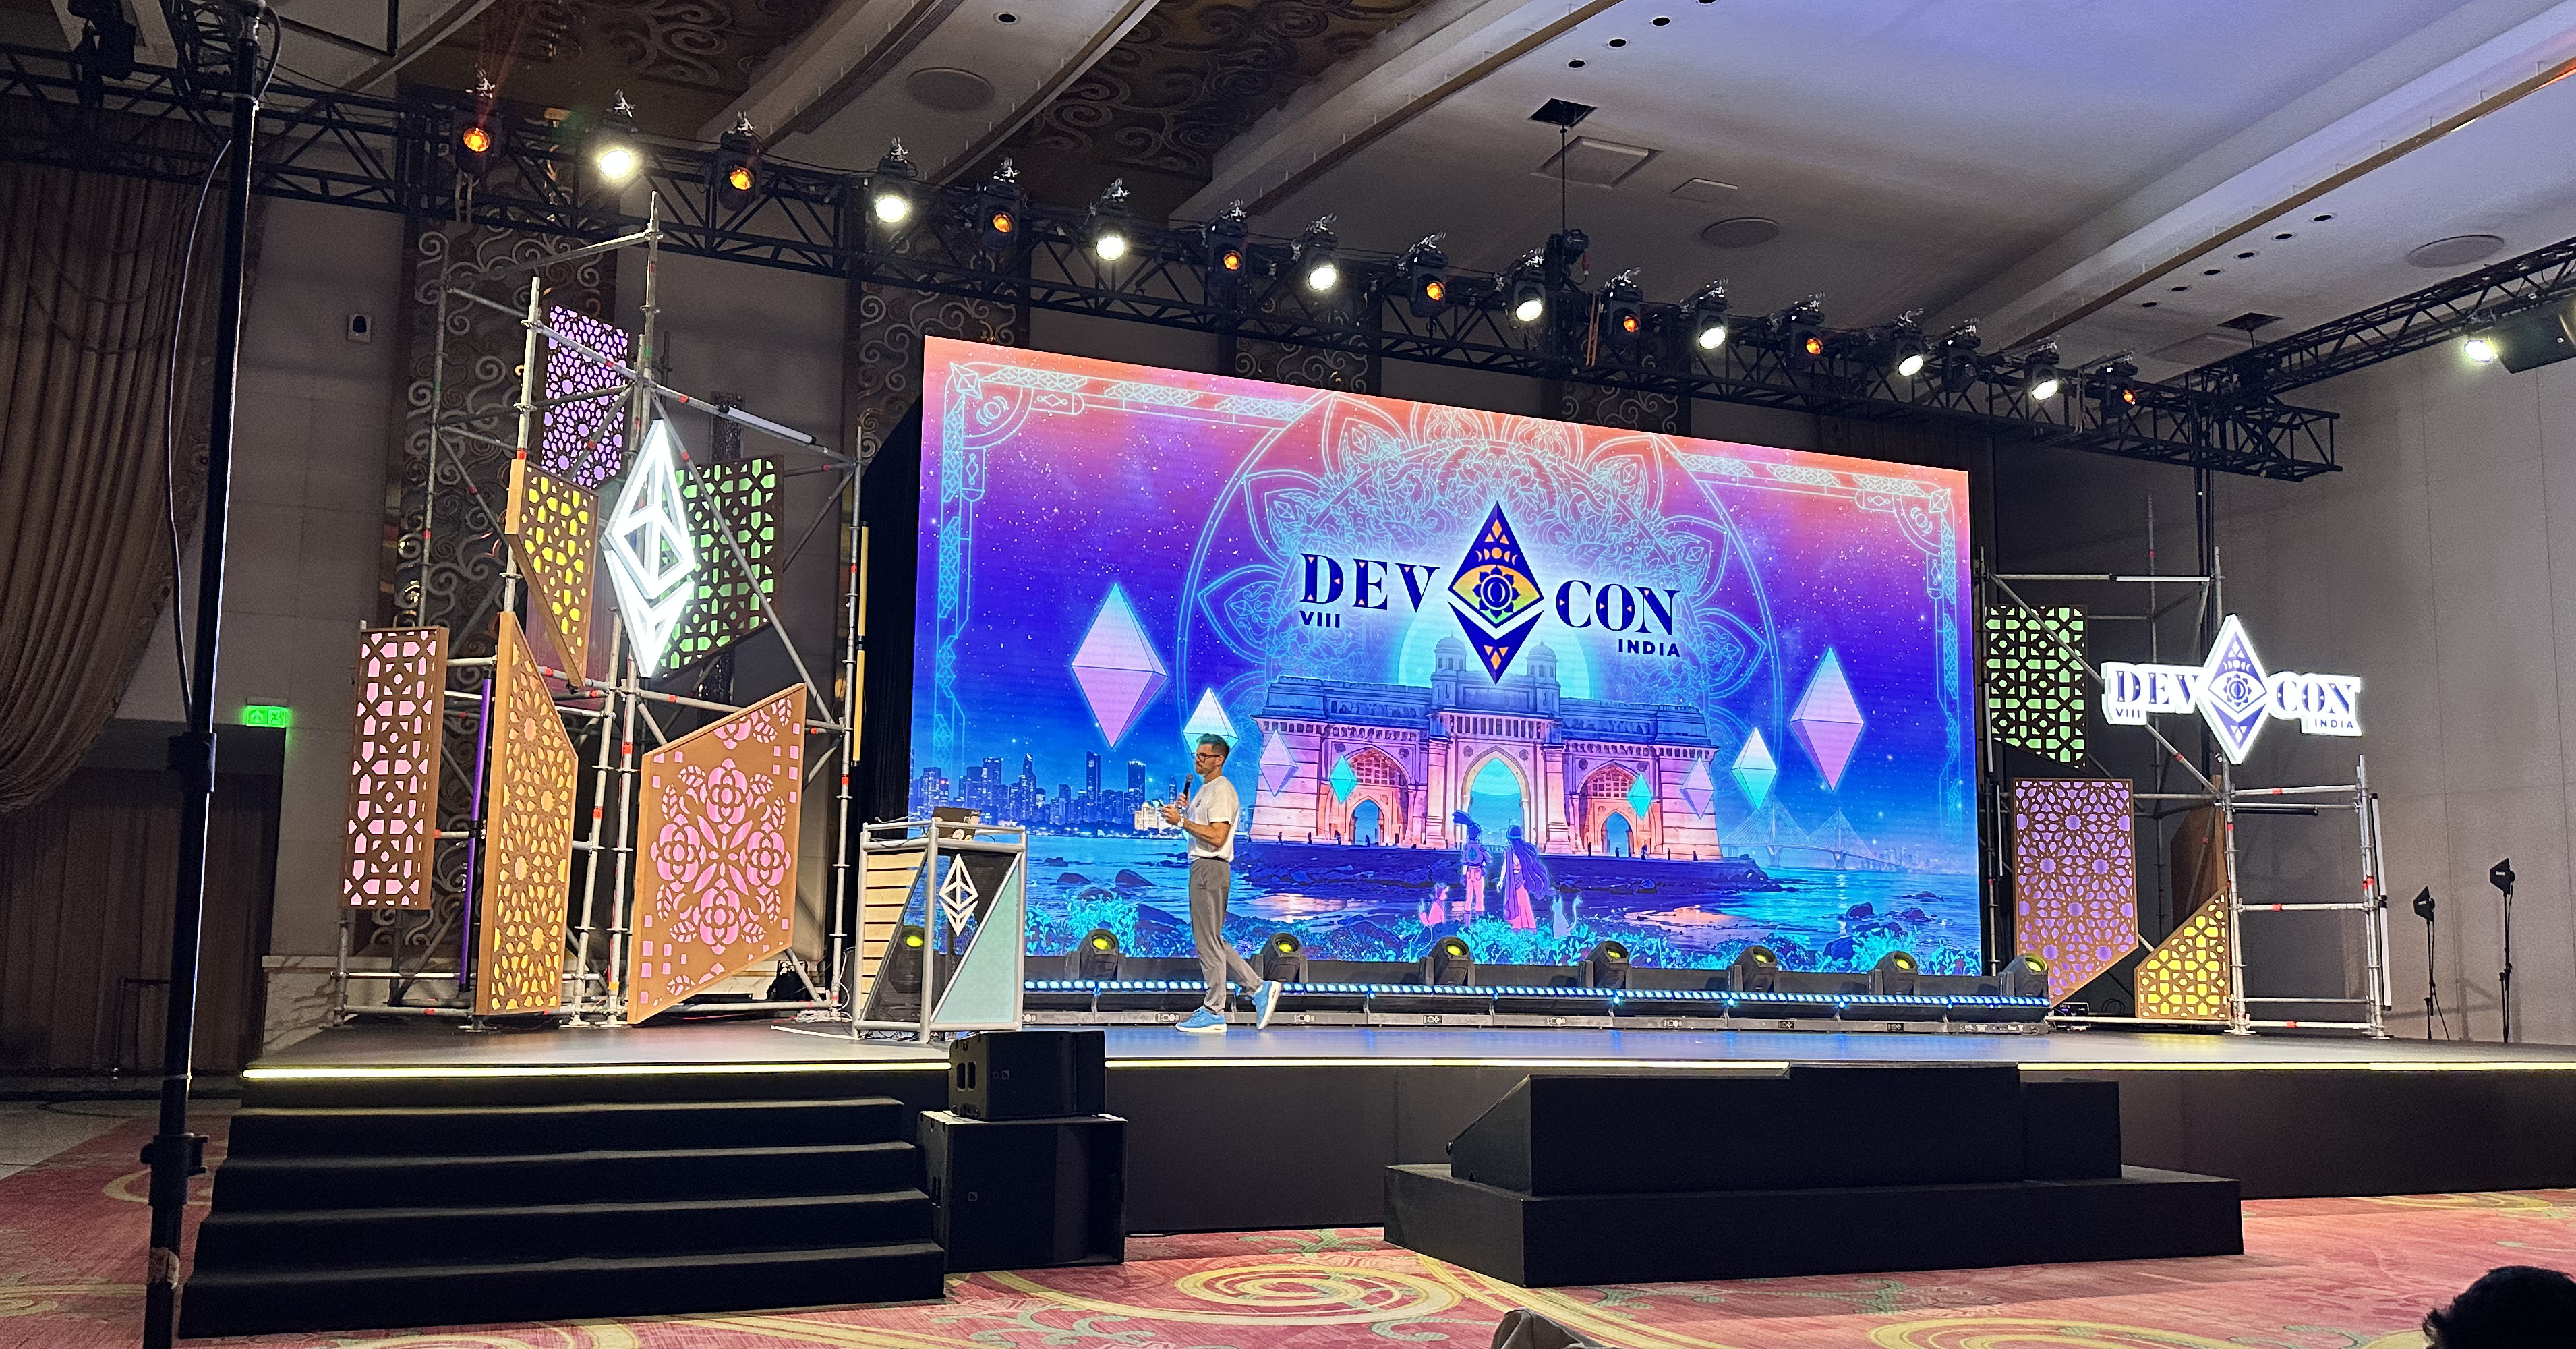
12 years of Devcon (/connect) attendance, first time representing Dark Bio! It has been a wonderful event like always, kudos to the organizer team, the volunteers and everyone coming to Mumbai to meet and greet.
We’ve been given the opportunity to do a few talks, and ended up accepting two slots only, to keep our own sanity :D Apologies for the ones we turned down, we really appreciated the possibility!
Practical Privacy Day
Our first talk was on the 5th of November, during the Practical Privacy day at the Privacy Hub. We’ve talked about the approach Dark Bio takes to keep sensitive personal health data secure, while at the same time allowing any untrusted application (whether written by humans or agents) to compute on.
It runs through the challenges of using LLMs to cross the chasm from high level biology questions a user might ask, down to the low level datasets they might have received from a sequencing laboratory; how all of that can be assembled into an ecosystem of interoperable puzzle-pieces; all whilst keeping LLMs hands off your data, guaranteed.
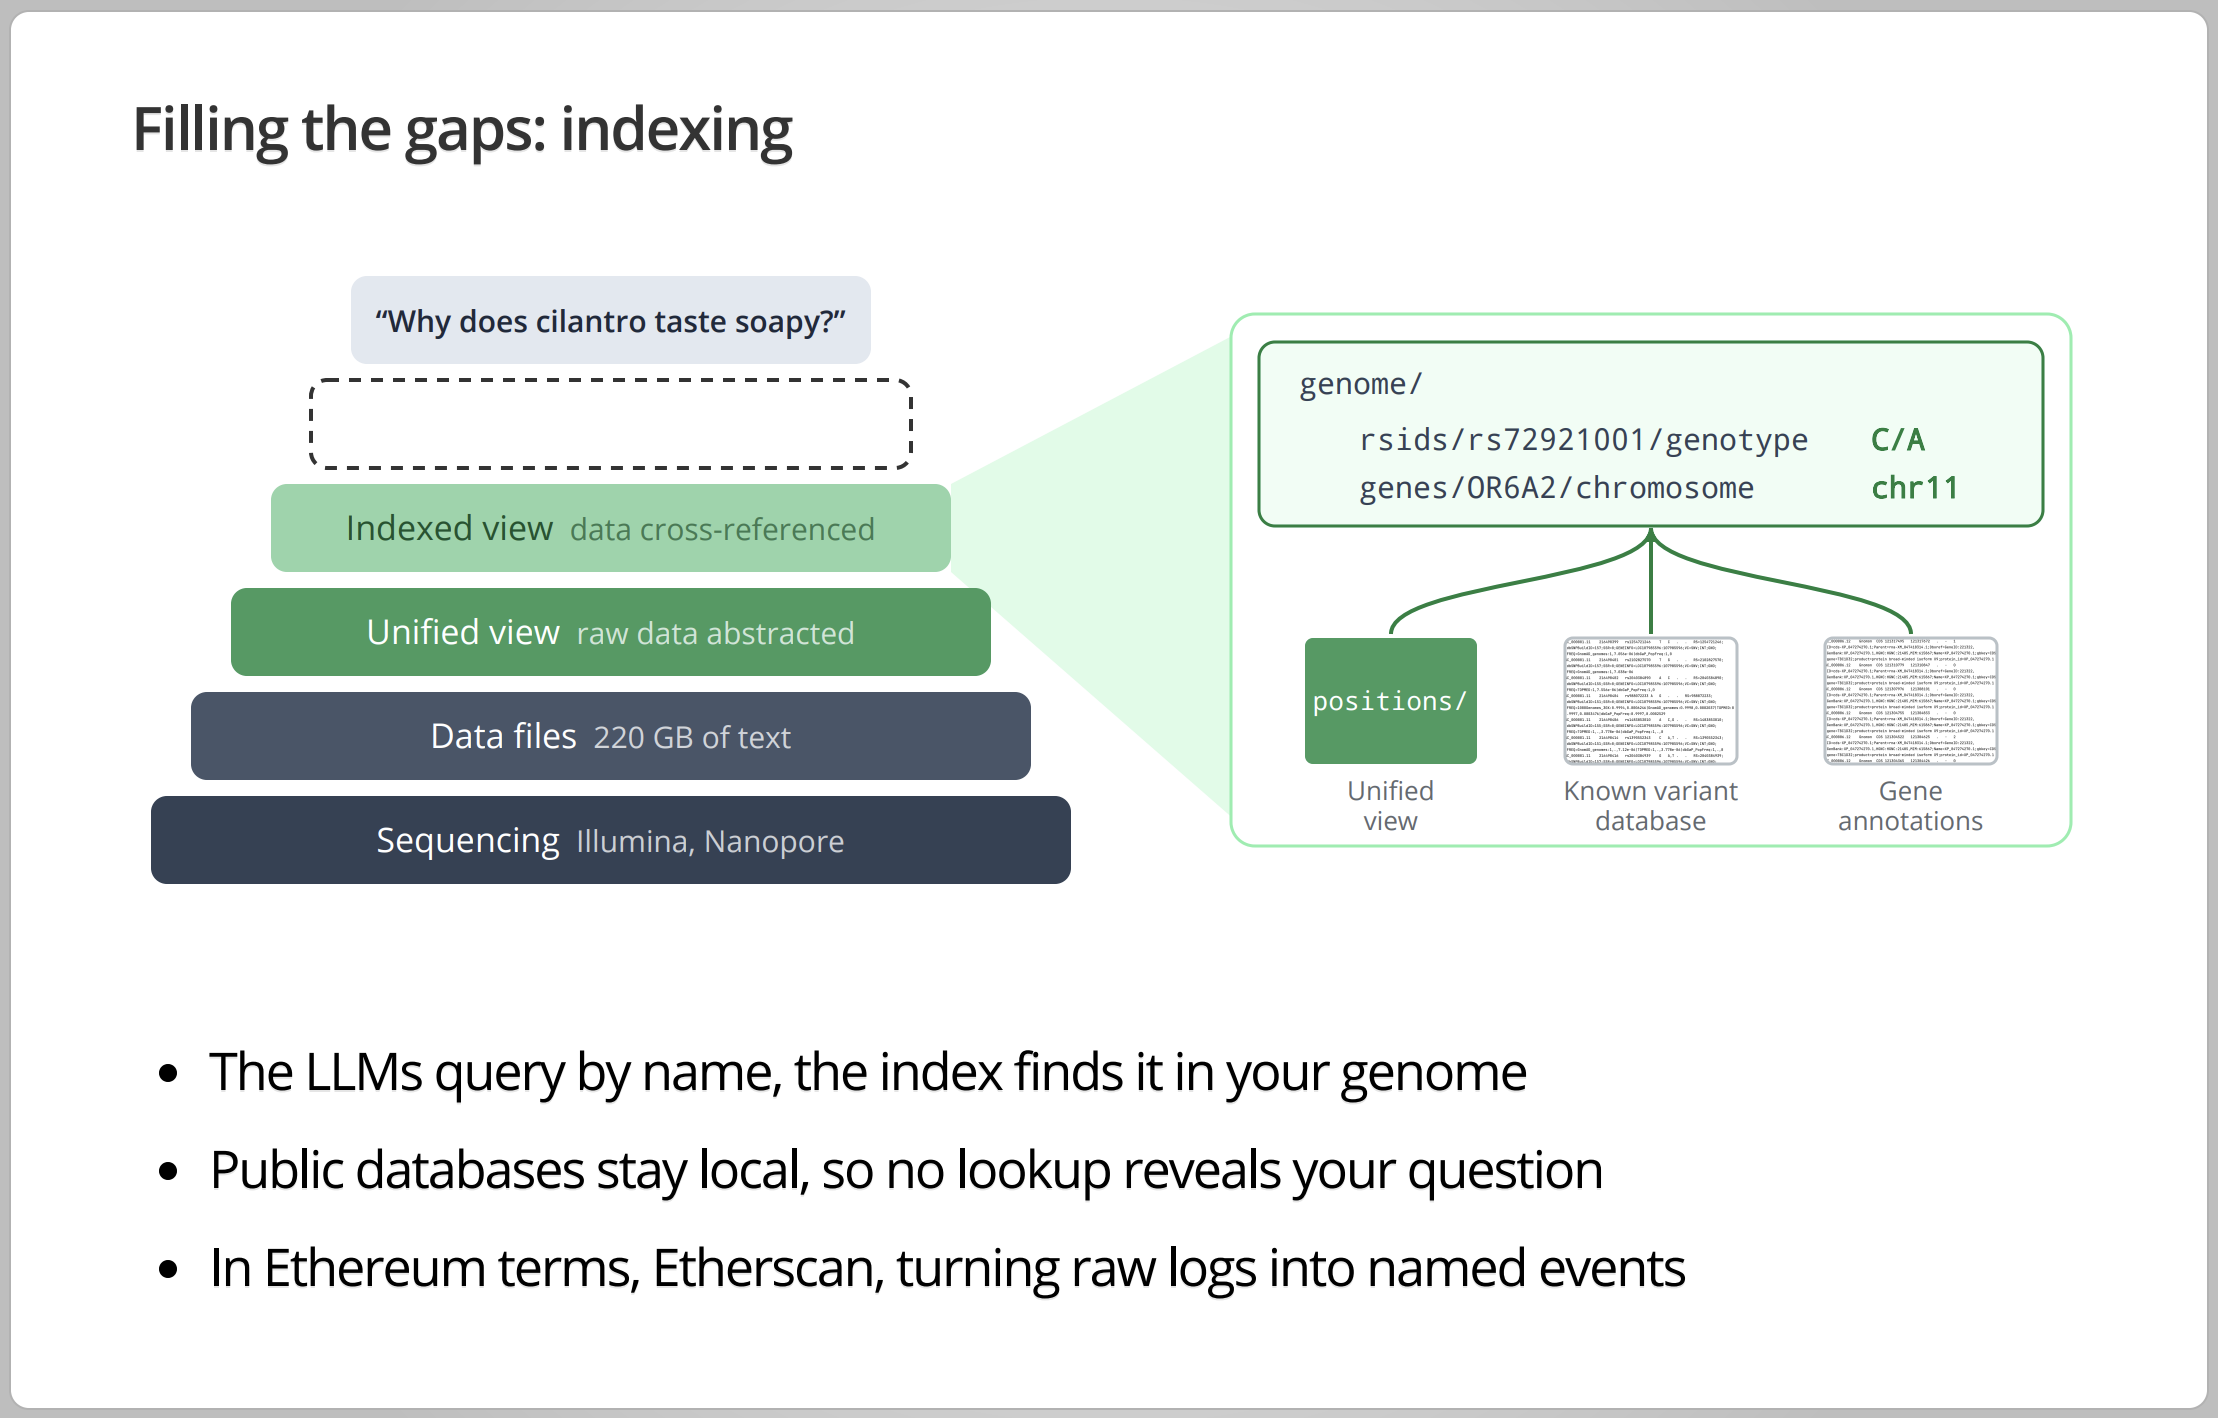
You can find the entire slide deck of the talk at:
Analyzing genomics in an agentic world
Redesigning health-tech from first principles
We’re unsure if there was a recording, most probably not. But we’ll add it to this blog post if it ever pops up!
Open and Verifiable Stack
Our second talk was on the 6th of November, within the Open and Verifiable Stack track, funnily being the closing talk for the entire conference! This talk was not about Dark Bio directly, rather about security research we did on breaking hardware security boundaries while hardening the Ark I!
Whilst we failed to break the security guarantees of the Ark (that’s good), we actually managed to find a number of denial-of-service and secure-boot escape vulnerabilities in the compute modules we ourselves use, escalating them into working exploits. These have been reported upstream and many are already fixed in new firmware releases.
Watching LLMs operate on breaking the hardware / firmware, however, was an eye-opening experience, so our talk was presenting this flow, in a slightly simplified view for easier understanding.
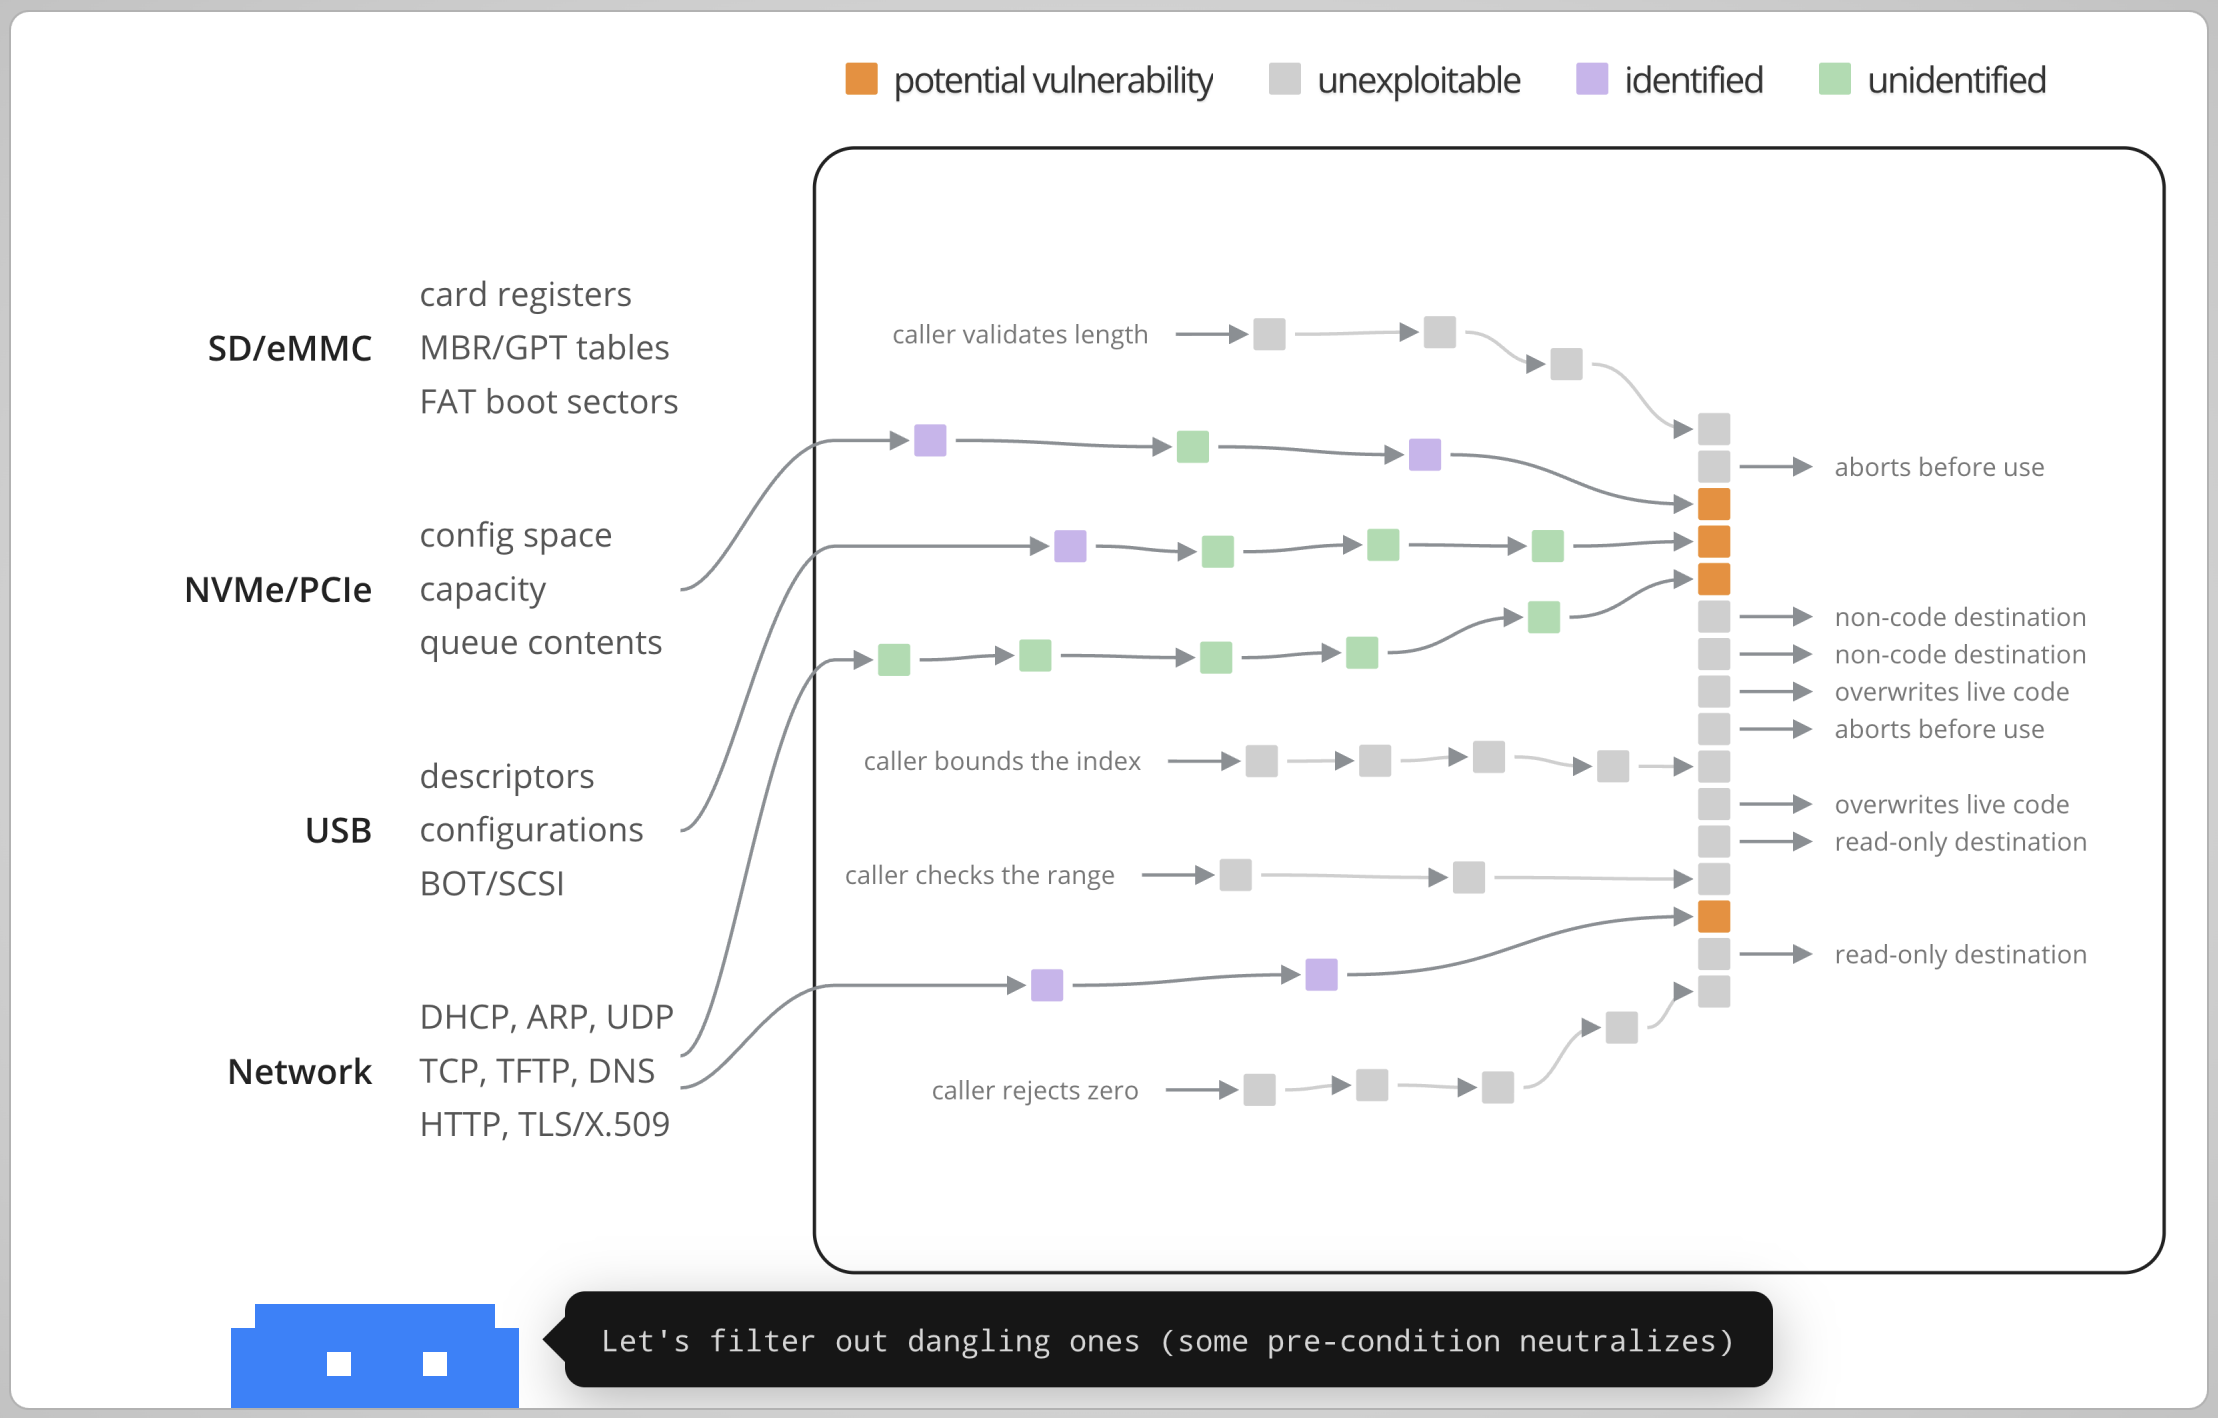
We’ve put a lot of effort into making this one a fun talk, both story and visuals wise, so you can find the entire original animated slide deck at:
Security by obscurity is dead
How LLMs can take over hardware
The deck needs to load fully for it to be properly active. On slow links or less capable devices, you might want the pdf deck.
This particular talk is already available online, so go have a watch! Was a blast making and presenting it!
Devcon 8 Ark giveaway
Last, but not least, we’ve had a small giveaway organized for this year’s
Devcon, featuring a special edition Ark I with the Devcon 8 logo etched in,
and having the unique serial number founder-devcon-8.
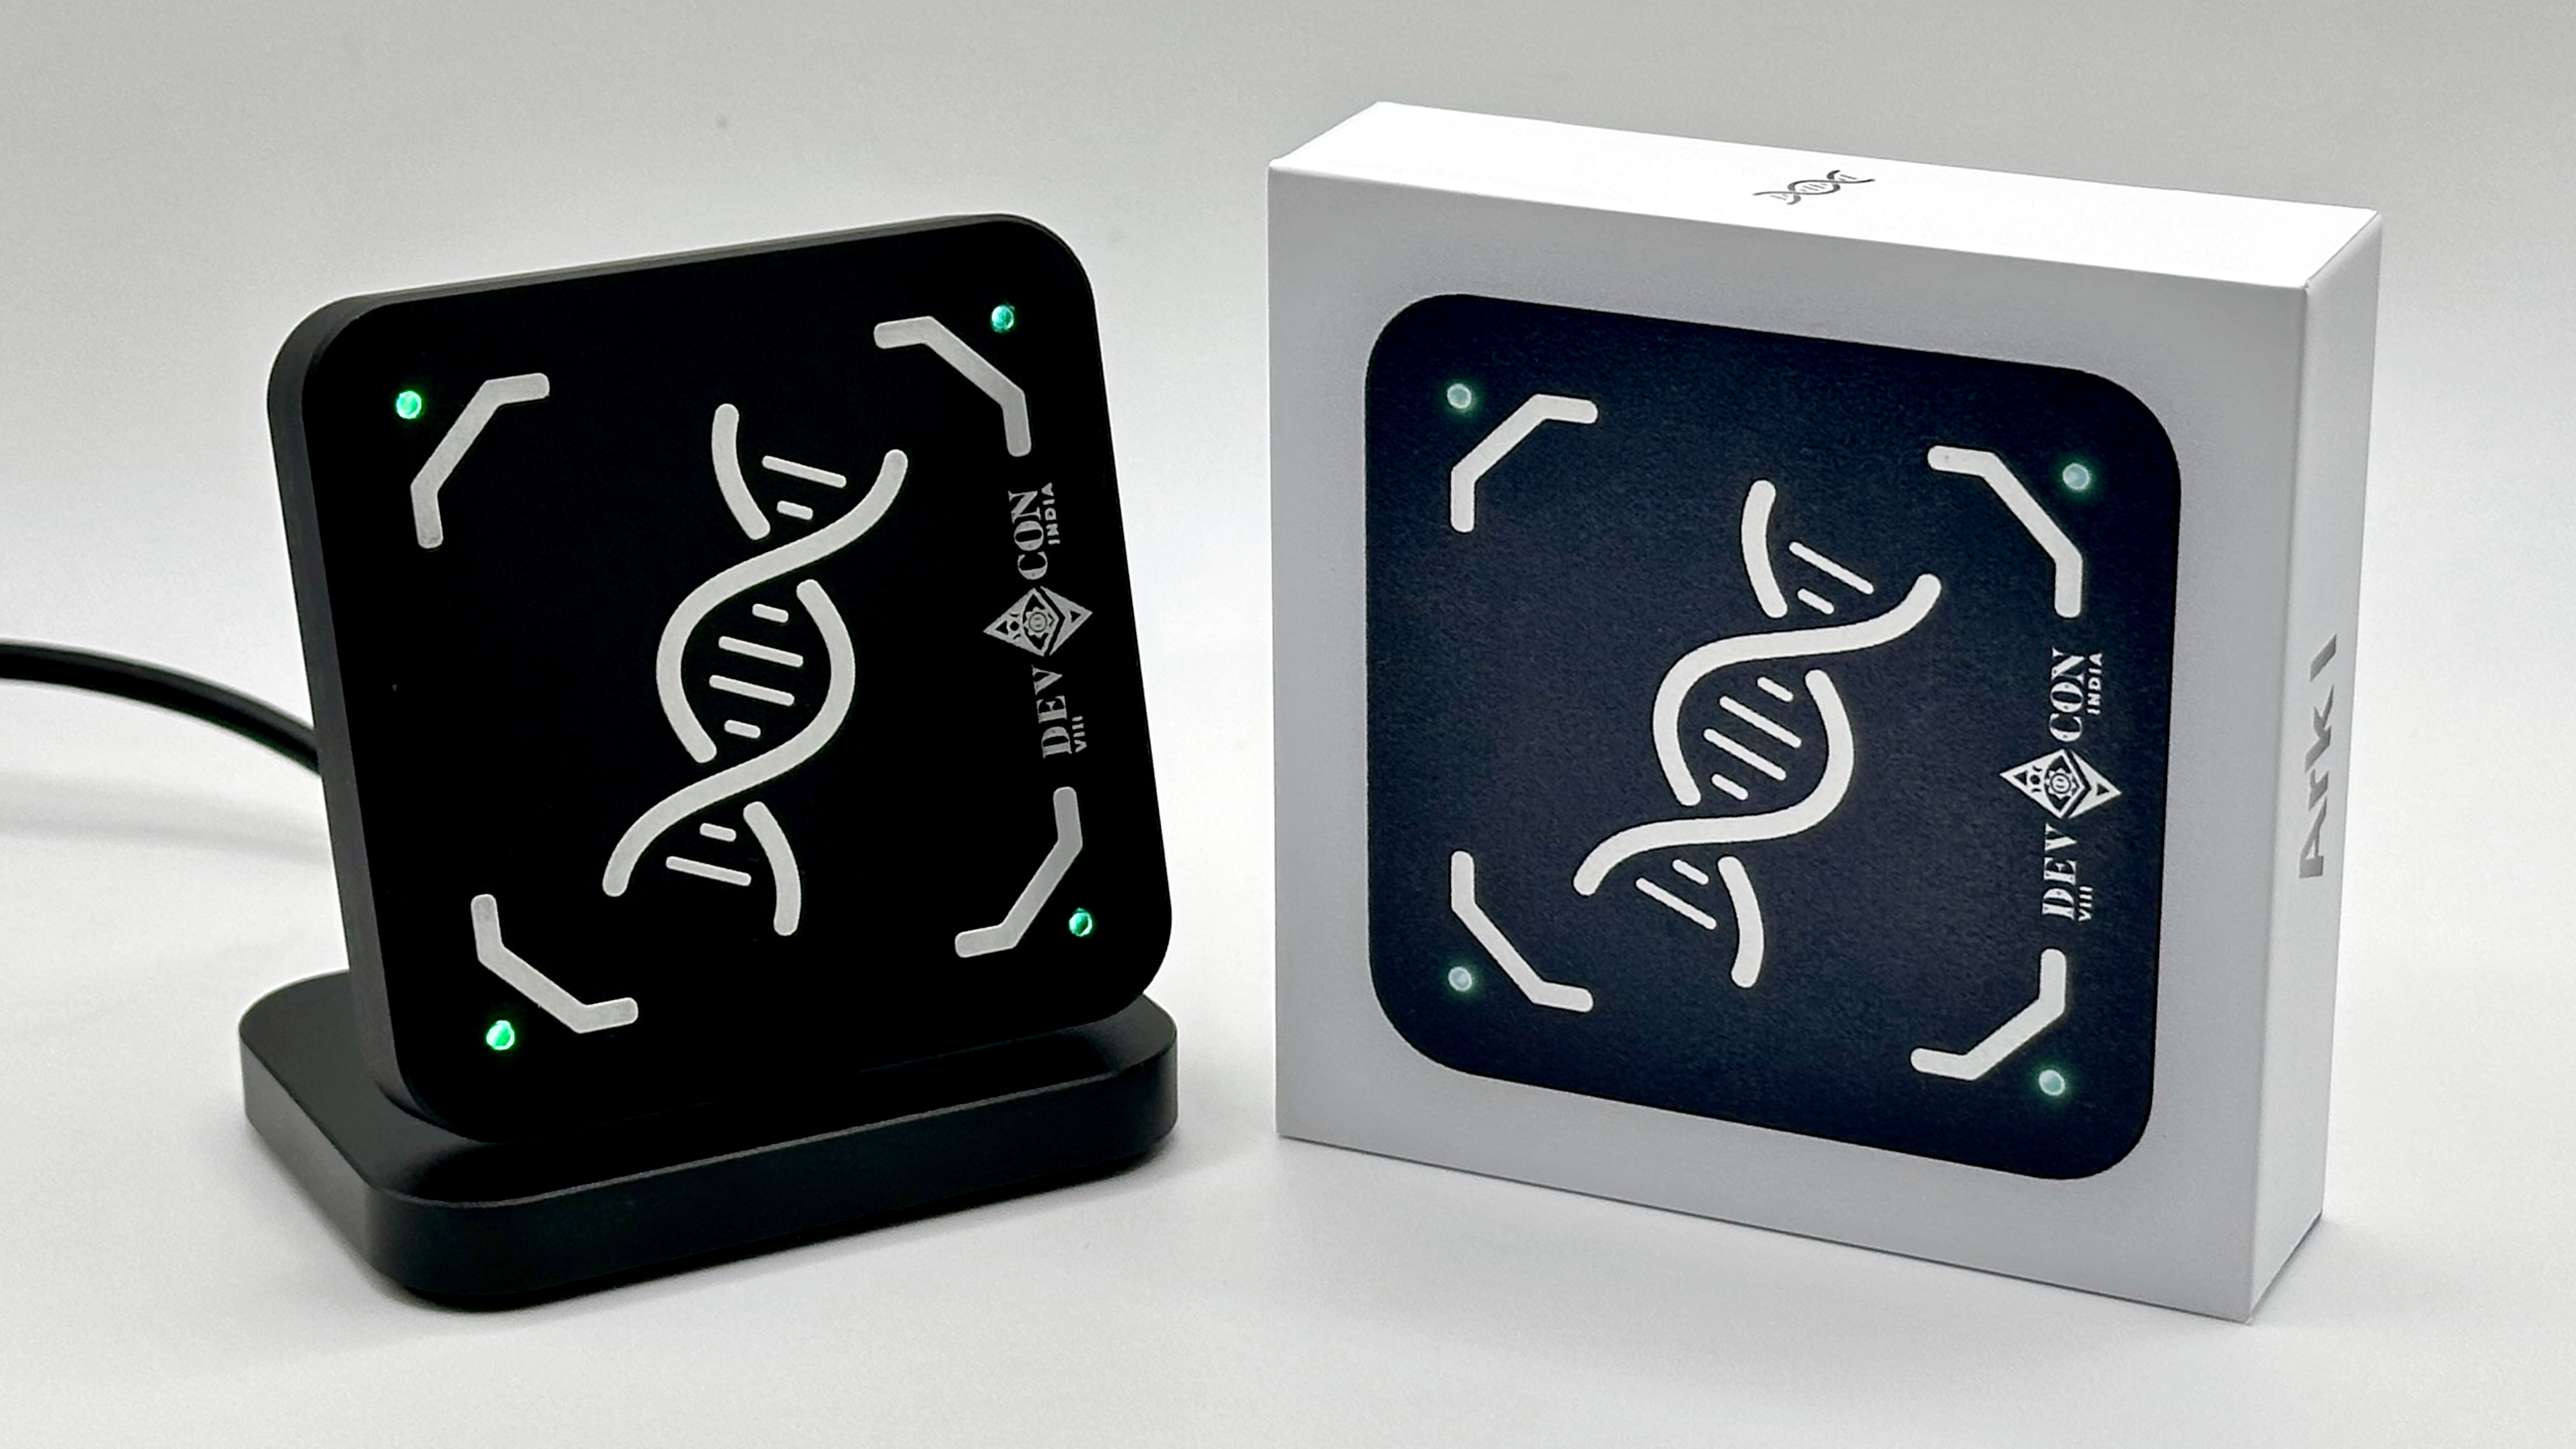
To avoid farming it, we’ve commited to the giveaway rules through an X post and the Dark Bio newsletter, but have not revealed the actual rule:
sha256("<rule>") = 96ddf7beed0ee97a04f7cf05314eb1e4f530b322cfc80223b738a36ca20e0da0
The rule was:
% sha256 -s "The Devcon 8 founder Ark will be gifted to the person who asks the most upvoted on-topic question at Peter's talk on the Practical Privacy day. If questions aren't upvoted, the gift goes to the thorniest one as decided by Peter on the spot. SALT(3ff9c823e5e605014ad67f2847d17002)"

96ddf7beed0ee97a04f7cf05314eb1e4f530b322cfc80223b738a36ca20e0da0
As there were no upvotes, the tie-breaker kicked in and Syed Asad Kazmi’s question was chosen, who asked how we handle the scenario when the user’s phone gets stolen / lost / breaks, taking the half encryption key with it.
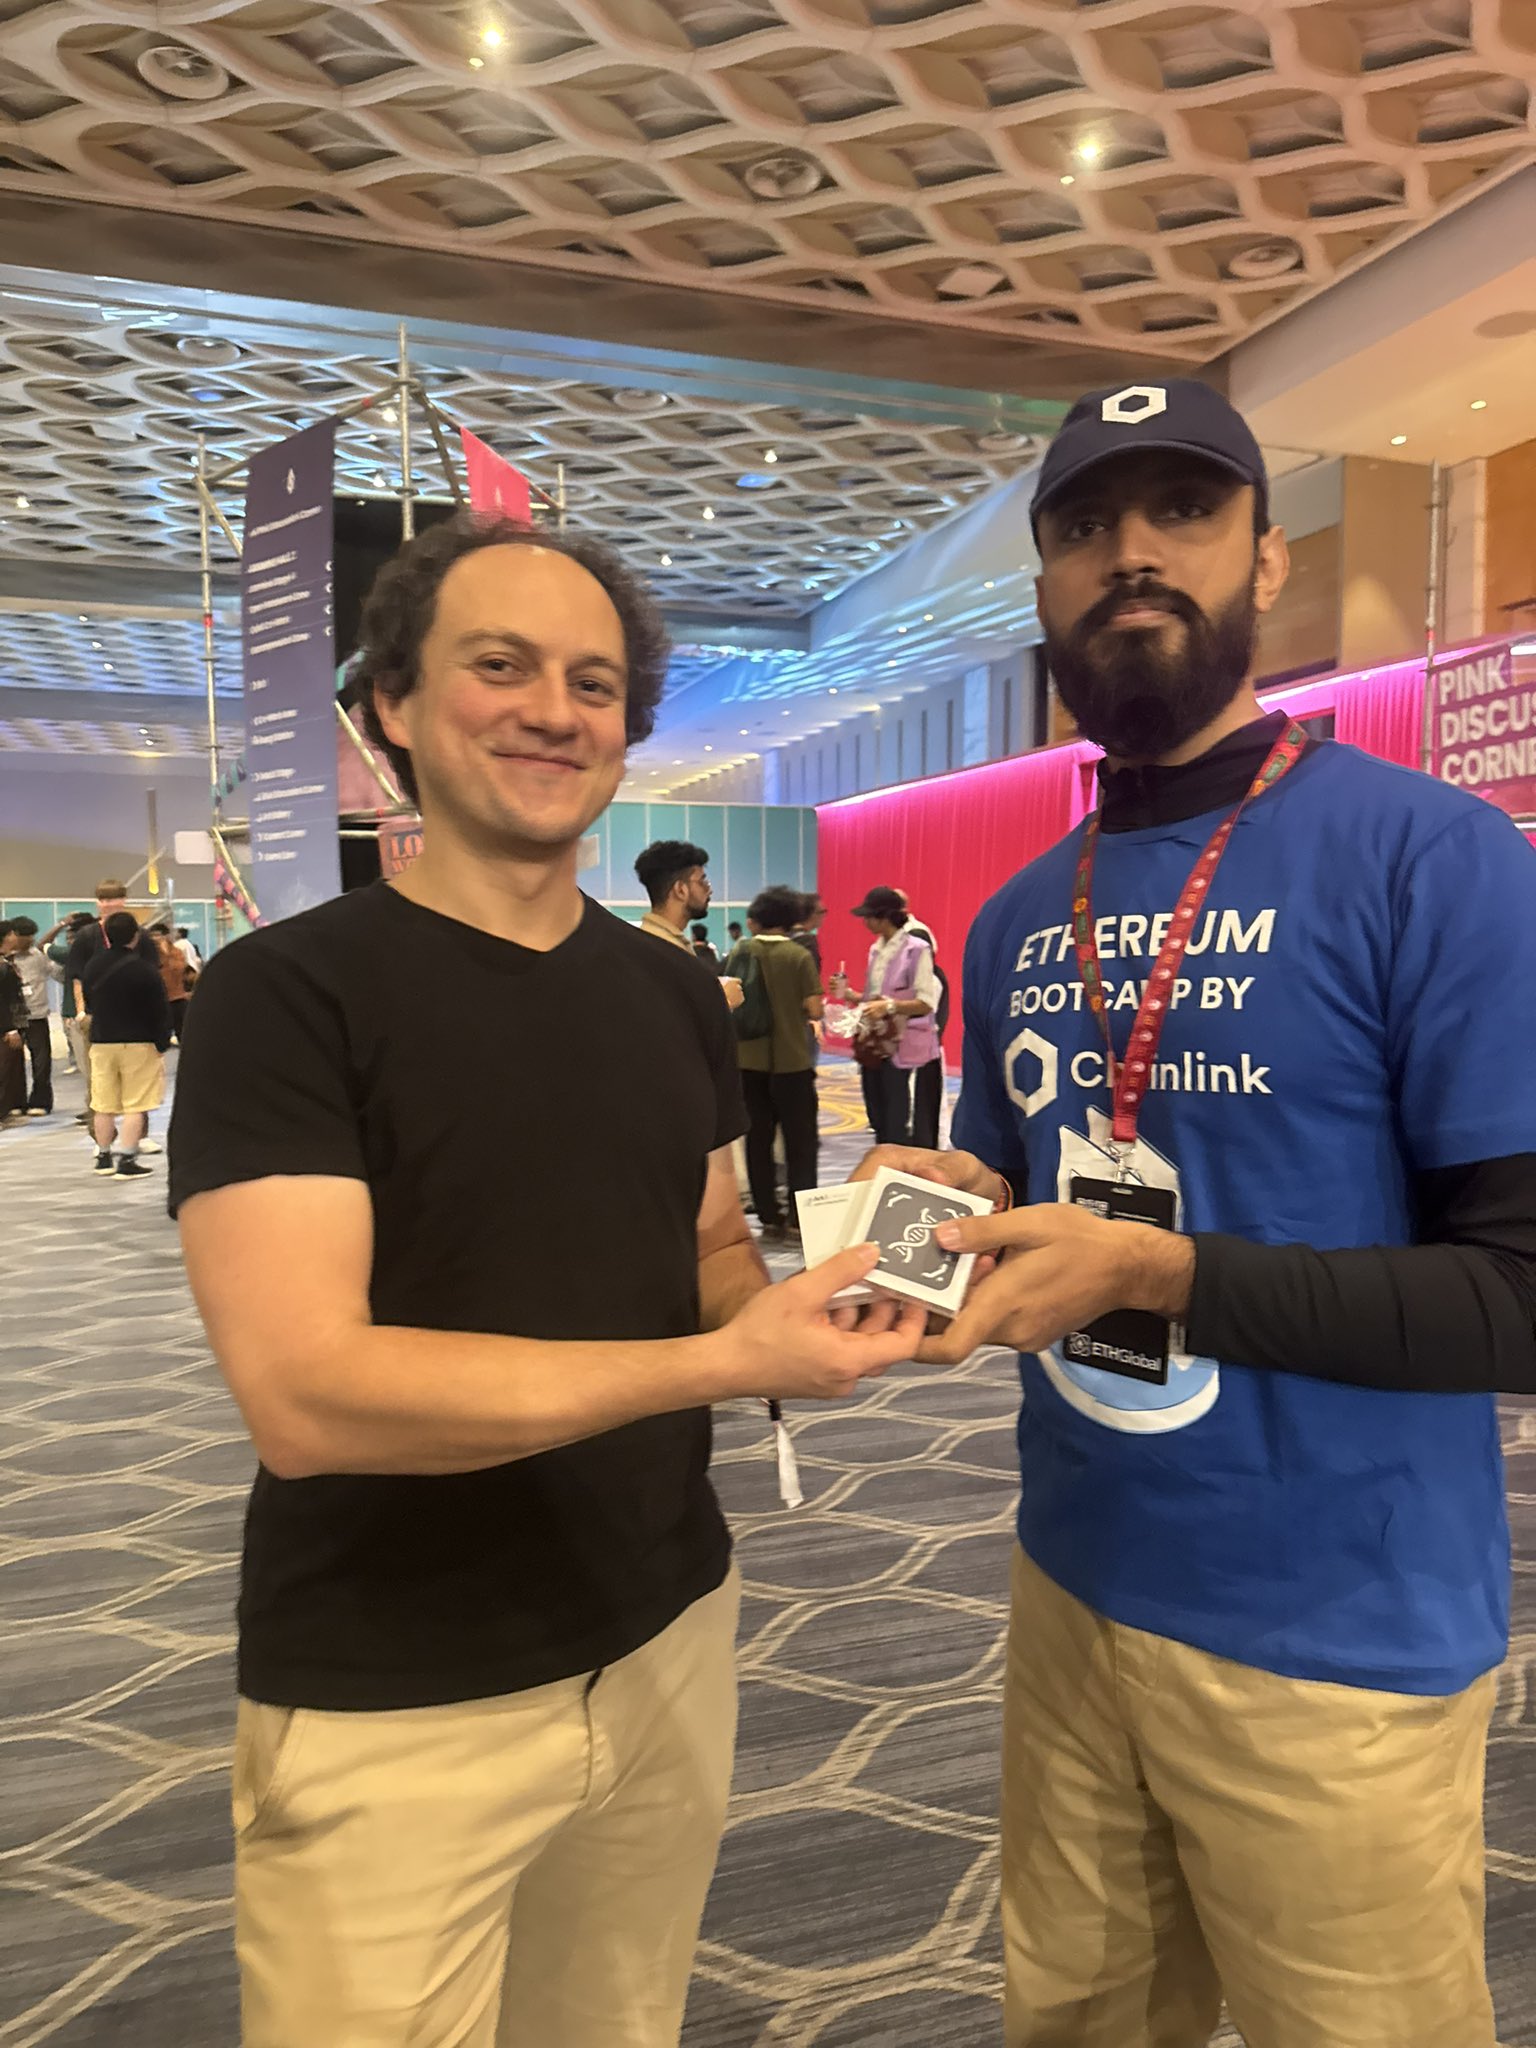
Thank you for coming to the talk and poking holes at the project! May the Ark bring you fun hacking sessions :)
Until next time…
#devcon #talk #privacy #security #agent #ark #hardware #genomics